An ISO 27001 trust center for UK and EU buyers
Notice Labs gives you a public page for your ISO/IEC 27001 status, at your own domain. The certificate is public, the Statement of Applicability or audit report goes out on request, and the status you show is the one you're actually at.
From £39 a month. No sales call.
A questionnaire asks about ISO 27001 before it asks anything else
UK and EU buyers ask for ISO/IEC 27001 status earlier than most other frameworks. The usual answer is a PDF certificate emailed on request, or a line in a spreadsheet, and the reviewer still has to chase the Statement of Applicability or the audit report separately.
The same buyers often want to see the family around 27001 too: 27017 for cloud services, 27018 for personal data, 27701 for a privacy information management system. Listing them one at a time, in email threads, slows the same review down again for every deal.
How it works
- 01
Set your status
Add ISO/IEC 27001 to your trust center's compliance list, and 27017, 27018 or 27701 alongside it if they apply. Mark each one certified, aligned or in progress, with an optional note.
- 02
Publish the certificate
Upload the certificate as a public document. Anyone visiting your trust center can see it without asking.
- 03
Gate the rest
Add the Statement of Applicability or the audit report as a document that needs a request: a file upload or a link, marked with its kind and effective date.
- 04
Approve requests
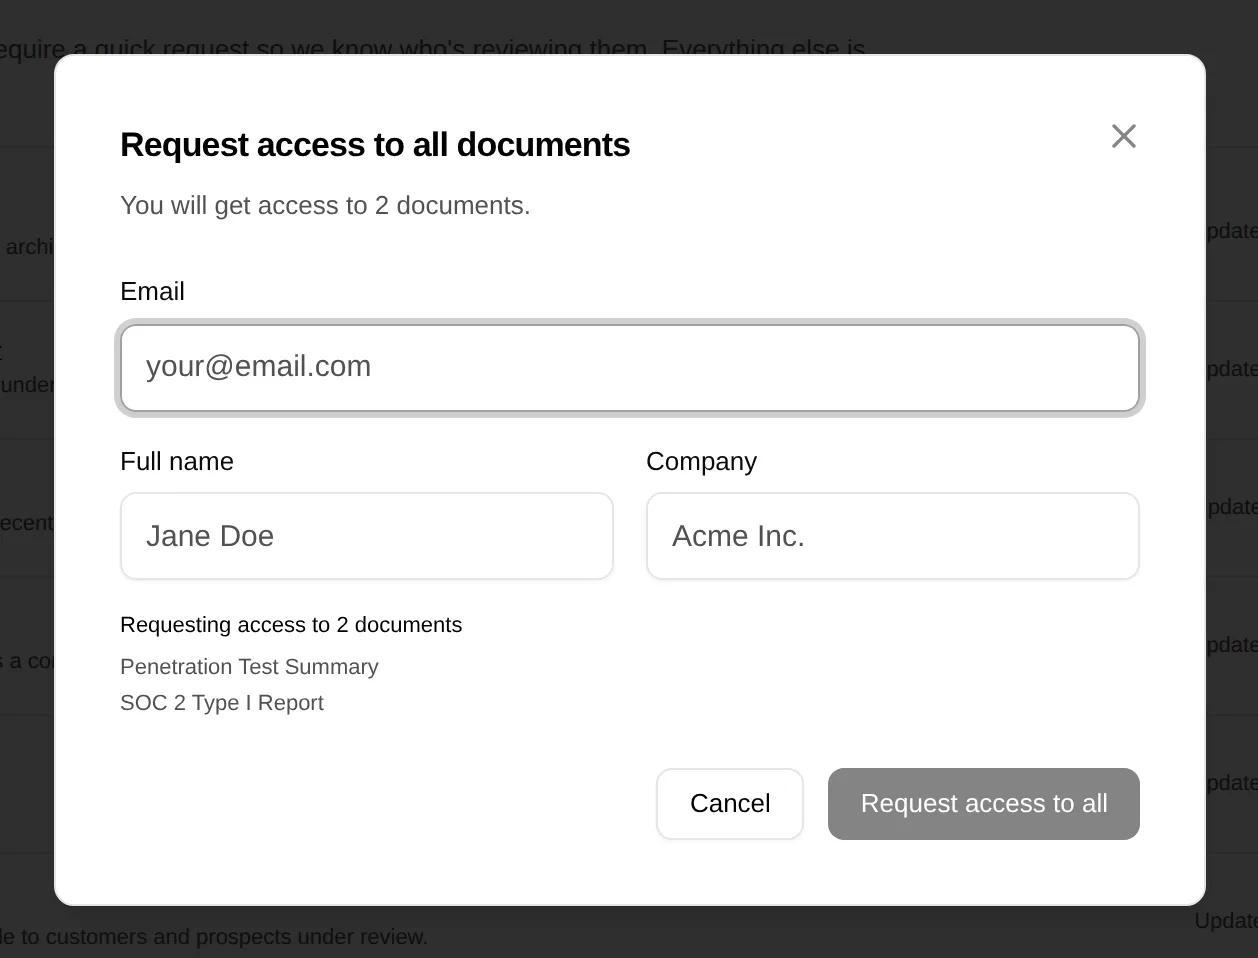
A buyer gives their name, company and email and picks the documents they want. You approve or deny each request in the admin; an approved link expires after 30 days.
The certificate stays public; the rest is a request away
Documents sit in one list with their kind and effective date. The certificate is set to public so it loads straight away; the Statement of Applicability or the full audit report is set to available on request, so it's there without being open to anyone who finds the page. You can revoke an approved link at any time.
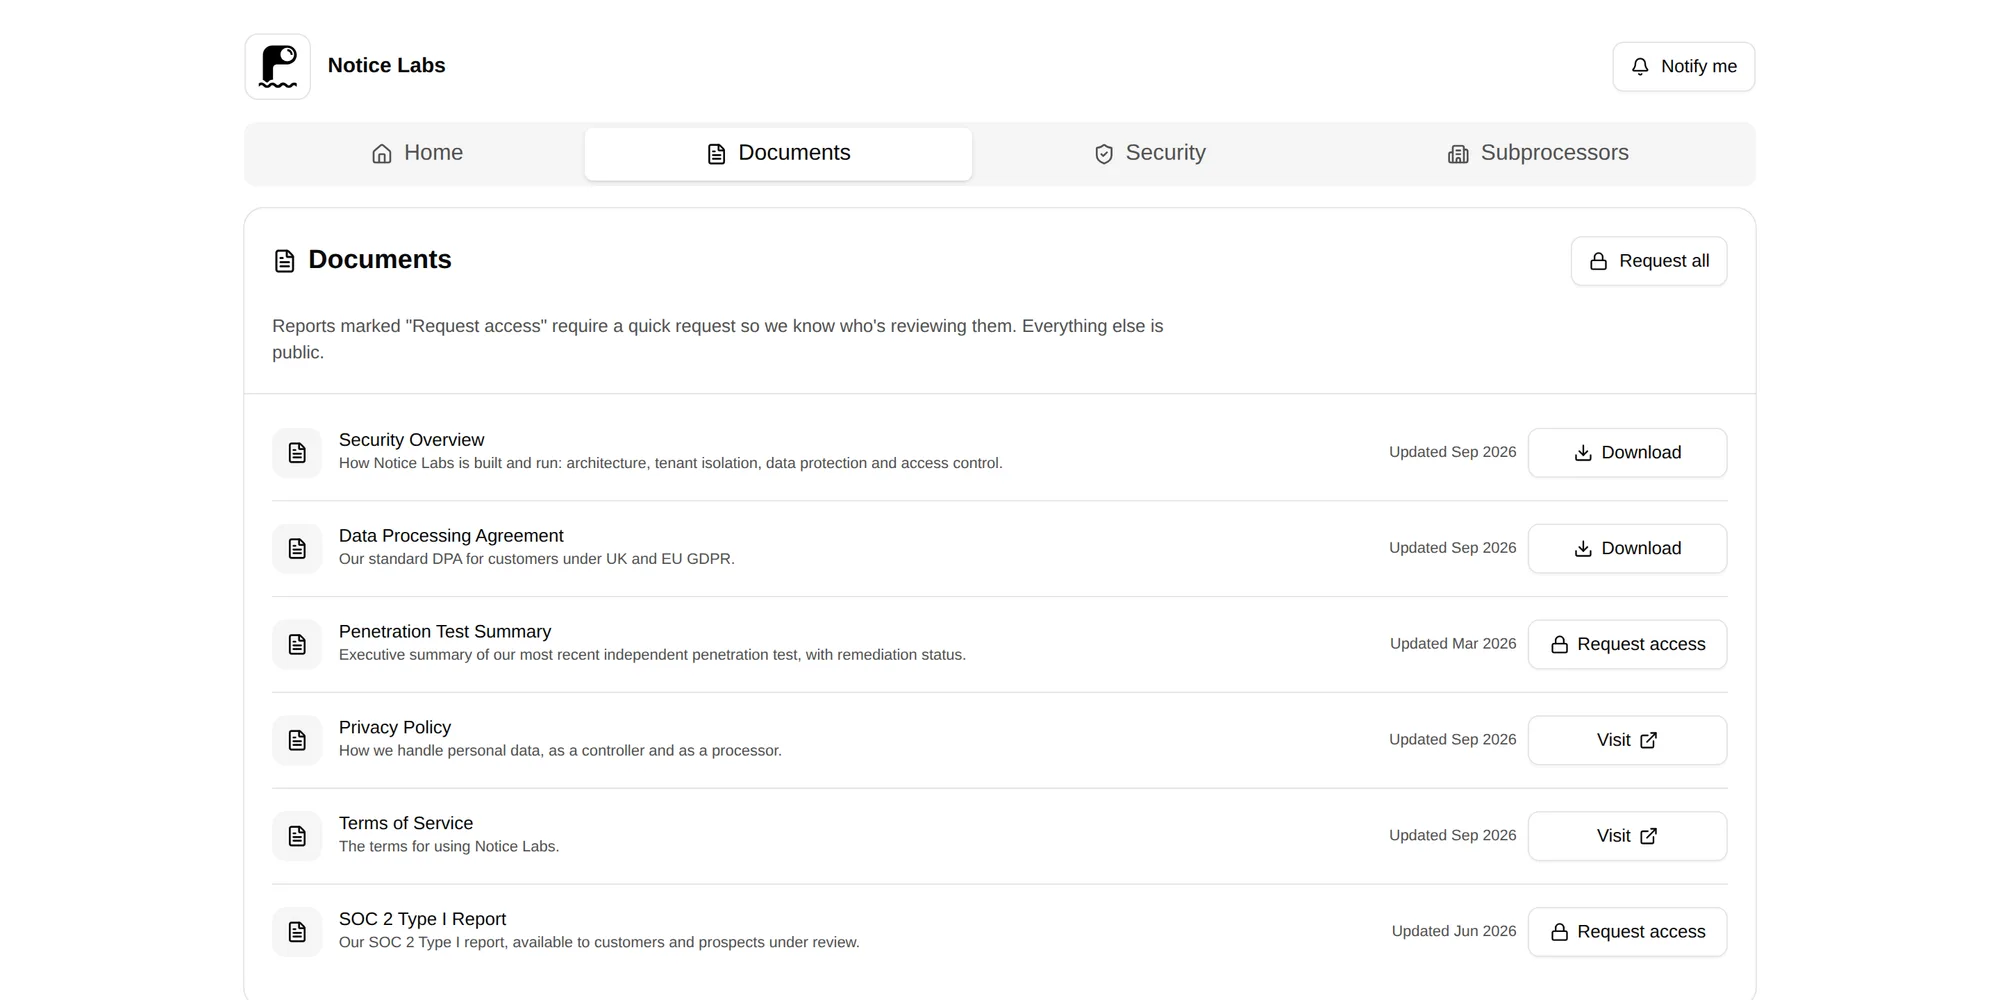
A request that gives you a name, not just a download
A buyer picks what they need and gives their email, name and company. You see who's asking before you approve it, and the record stays in the admin rather than in an inbox.
What's on the page
- Compliance statusISO/IEC 27001, 27017, 27018 and 27701 each shown with their own status, so a reviewer isn't guessing which parts of the family apply to you.
- Gated documentsThe certificate public, the Statement of Applicability or audit report behind a request, with an approval step before anything goes out.
- Security controlsThe controls behind your certification, in plain language, so a reviewer sees more than a status badge.
- Cyber EssentialsSell to UK buyers? List Cyber Essentials next to ISO 27001, and see what it covers and what changed in 2026.
- Subprocessor listThe vendors in scope for your ISMS, with their purpose and location, which an ISO 27001 review usually asks for too.
What it doesn't do
Notice Labs doesn't audit you against ISO/IEC 27001, issue or verify a certificate, or run the ISMS behind it. The status you set is the one you attest to; Notice Labs displays it, it doesn't check it against your certification body.
It's a way to publish where you stand and share the paperwork behind it without an email thread. Getting certified, or extending certification to 27017, 27018 or 27701, is still work you do with your certification body.
Questions
Straight answers to what people ask before they set this up.
Can I publish the certificate without exposing the Statement of Applicability?
Yes. Set the certificate to public and the Statement of Applicability, or the full audit report, to available on request. Each document has its own visibility, so you choose what's open and what needs a name and email first.
Do I need to be certified already?
No. You can mark ISO/IEC 27001 as in progress or aligned, with a note on where you are, rather than certified. Buyers who ask early in a sales cycle usually just want an honest answer.
Does this cover 27017, 27018 and 27701 as well as 27001?
Yes. Each one is a separate line in your compliance list with its own status, so you can show a cloud-security extension, a personal-data extension or a privacy management system alongside the base certification, or on its own.
Who sees a document request before it's approved?
Your team, in the admin. A request lists the requester's name, company, email and the documents they picked; you approve or deny each one, and an approved link expires after 30 days. You can revoke it at any time.
Does Notice Labs audit or certify us for ISO 27001?
No. Notice Labs isn't a certification body and doesn't run the audit. It's where you publish the status and the paperwork once your certification body has done the work.
Is this suitable for UK and EU buyers?
Yes. The page states your status and scope in plain terms and gates the sensitive documents, which is what most UK and EU procurement reviews are checking for before they move on to the rest of the questionnaire.
Related reading
Publish your ISO 27001 status where buyers already look.
From £39 a month. No sales call.